The hazards a plant actually faces
The list is shorter than it looks, because most industrial incidents trace to a handful of recurring conditions. What differs between plants is which of them dominate.
- Combustible gas and vapour - LPG, solvent and fuel vapour, anything that will find an ignition source given a large enough cloud
- Toxic gas - carbon monoxide in particular, which is odourless and kills at concentrations well below anything a person will notice
- Smoke and flame - the hazard everyone plans for, and the one that is usually detected last because a smoke detector needs smoke to have already been produced
- Excess heat - both as a hazard and as the earliest available symptom of a machine that is about to fail
- Degraded air quality and chemical vapour - a chronic exposure problem rather than an acute one, and correspondingly easy to ignore
- Abnormal vibration - the classic mechanical-failure precursor, and one of the few signals that reliably appears before the failure rather than during it
- Abnormal sound - weak evidence alone, and a strong corroborating channel alongside heat and vibration
How a monitoring system works
The shape is consistent across implementations. Sensors sample the environment continuously. Each reading is compared against a threshold that defines what counts as abnormal. A breach raises an alarm locally, and typically also transmits to somewhere the event can be recorded and seen. Somebody acts.
The parts that separate a good system from a box on a wall are less obvious. Whether the thresholds are appropriate to that specific process, or generic. Whether the system establishes a baseline for that space rather than assuming everywhere is the same. Whether the alarm still works when the network does not. Whether the record is good enough to investigate an event afterwards. And whether alerts reach a person who can act, rather than a screen nobody is watching at 2am.
Single-point detectors and their limits
The conventional approach is one detector per hazard: a smoke detector, a gas detector, a heat sensor, each with its own threshold and its own alarm. It works, it is well understood, and it is what certification regimes are built around.
It has two structural weaknesses. The first is cost - eleven hazards means eleven instruments plus the wiring and the calibration regime for each, which is exactly why smaller plants end up with one smoke detector and a fire extinguisher.
The second is that a single-channel detector cannot see a hazard that only exists in the relationship between channels. A motor drawing more current runs hotter, vibrates differently and sounds different, and none of those three changes may individually cross a threshold. Read together they are a machine about to fail. Read separately they are three sensors reporting nothing wrong.
Real-time versus predictive monitoring
Real-time monitoring reports the present: this reading, right now, against this limit. It is necessary and it is inherently late, because by the time a threshold is crossed the hazardous condition already exists.
Predictive monitoring adds the derivative. Fit a trend to recent readings, project it at the threshold, and you get an estimate of time to threshold - a warning while there is still time to act rather than time to evacuate. Comparing current behaviour against a learned baseline adds the other half: a reading that is unremarkable in absolute terms can be extraordinary for that room at that hour.
Neither replaces the other. Prediction without a threshold is a forecast nobody has to act on; a threshold without prediction is a report that arrives at the moment it stops being useful.
What good placement looks like
Placement determines whether any of the above matters. Gas behaves according to its density - lighter-than-air gases collect high, heavier-than-air ones pool low - so a detector at the wrong height is monitoring a volume the hazard will never reach. Airflow moves a plume away from where it was generated, which means a node positioned by convenience rather than by survey may sit in dead air.
This is why a deployment starts with a site survey rather than a mounting bracket, and why threshold tuning against the plant's actual process baseline is part of commissioning rather than an optional extra.
How Alfa HazardX approaches it
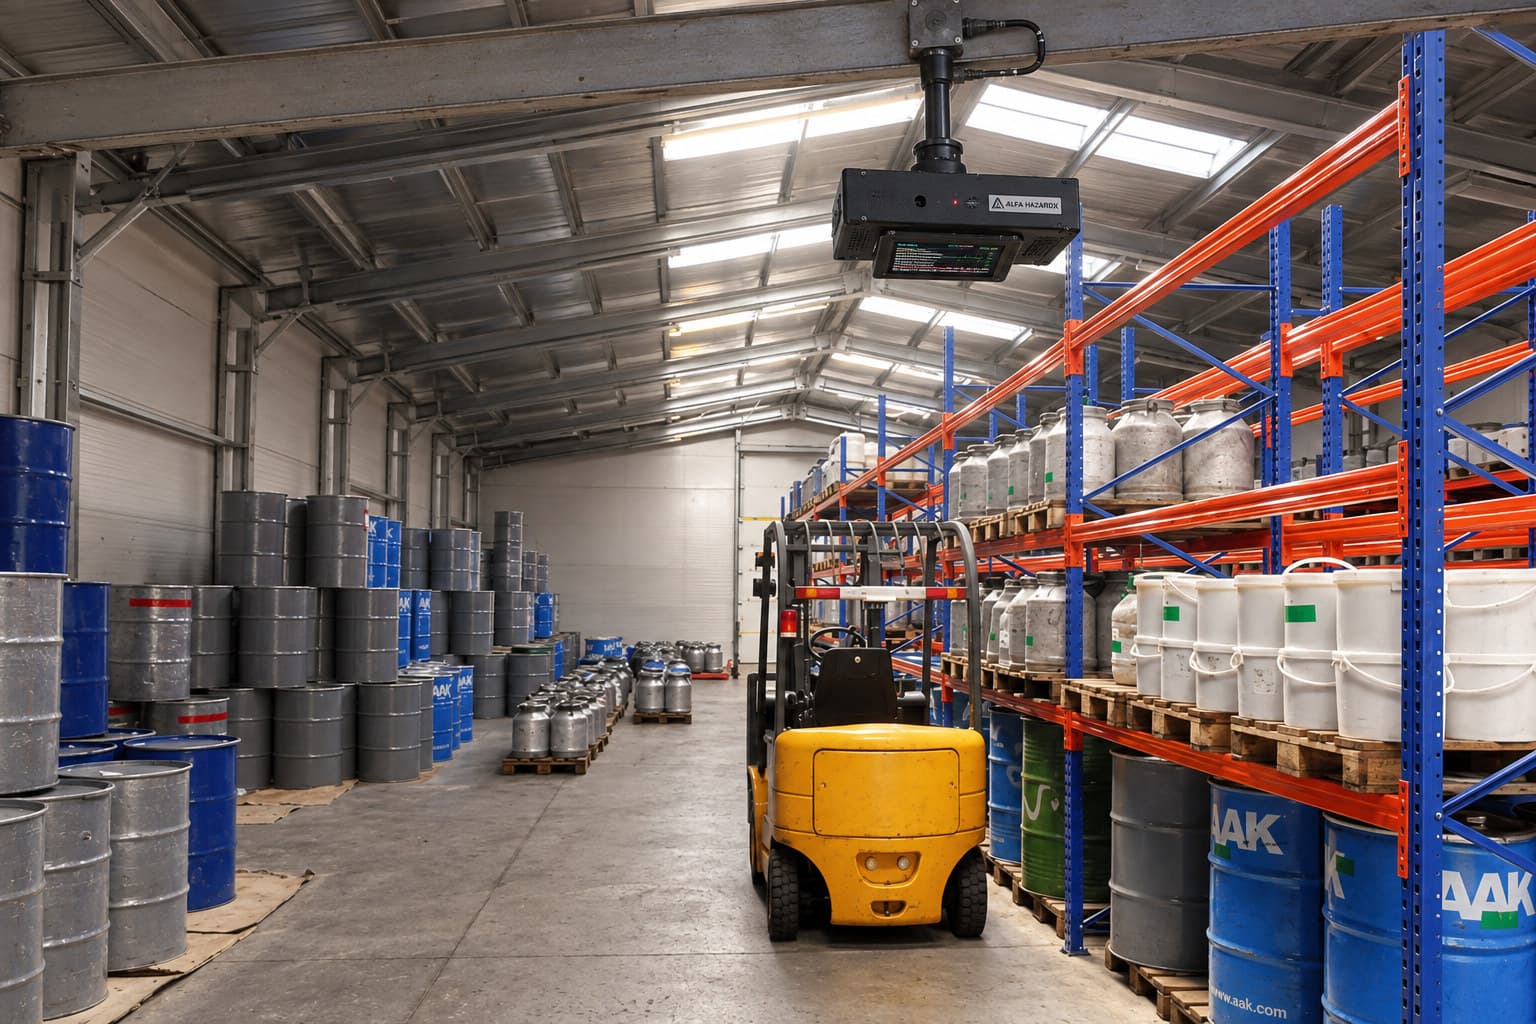
Alfa HazardX puts many channels on one node rather than one channel on many nodes: gas, flame, heat, air quality, vibration and sound sensed together, fused into a single risk state instead of read as separate alarms. Risk is classified deterministically on the device, so the local alarm survives a network outage. Trend and baseline analysis run in the cloud where there is enough history to be useful, and a generative model is used only to explain a decision the deterministic layer has already made.
It is a deployable V2 field node, not a certified instrument, and the pages linked below say exactly what that does and does not mean.